
HIPAA-Compliant AI Medical Translation & Interpretation
Secure, real-time voice-to-voice communication for US healthcare providers.
At Mabel AI, patient privacy is our foundational architecture. We provide highly secure, real-time medical translation that adapts to your organization’s IT infrastructure—whether you require rigorous on-premise control, secure SaaS deployments, or mobile accessibility.
Volatile In-Memory Processing | Zero Data Written to Disk | Fully Covered by our BAA
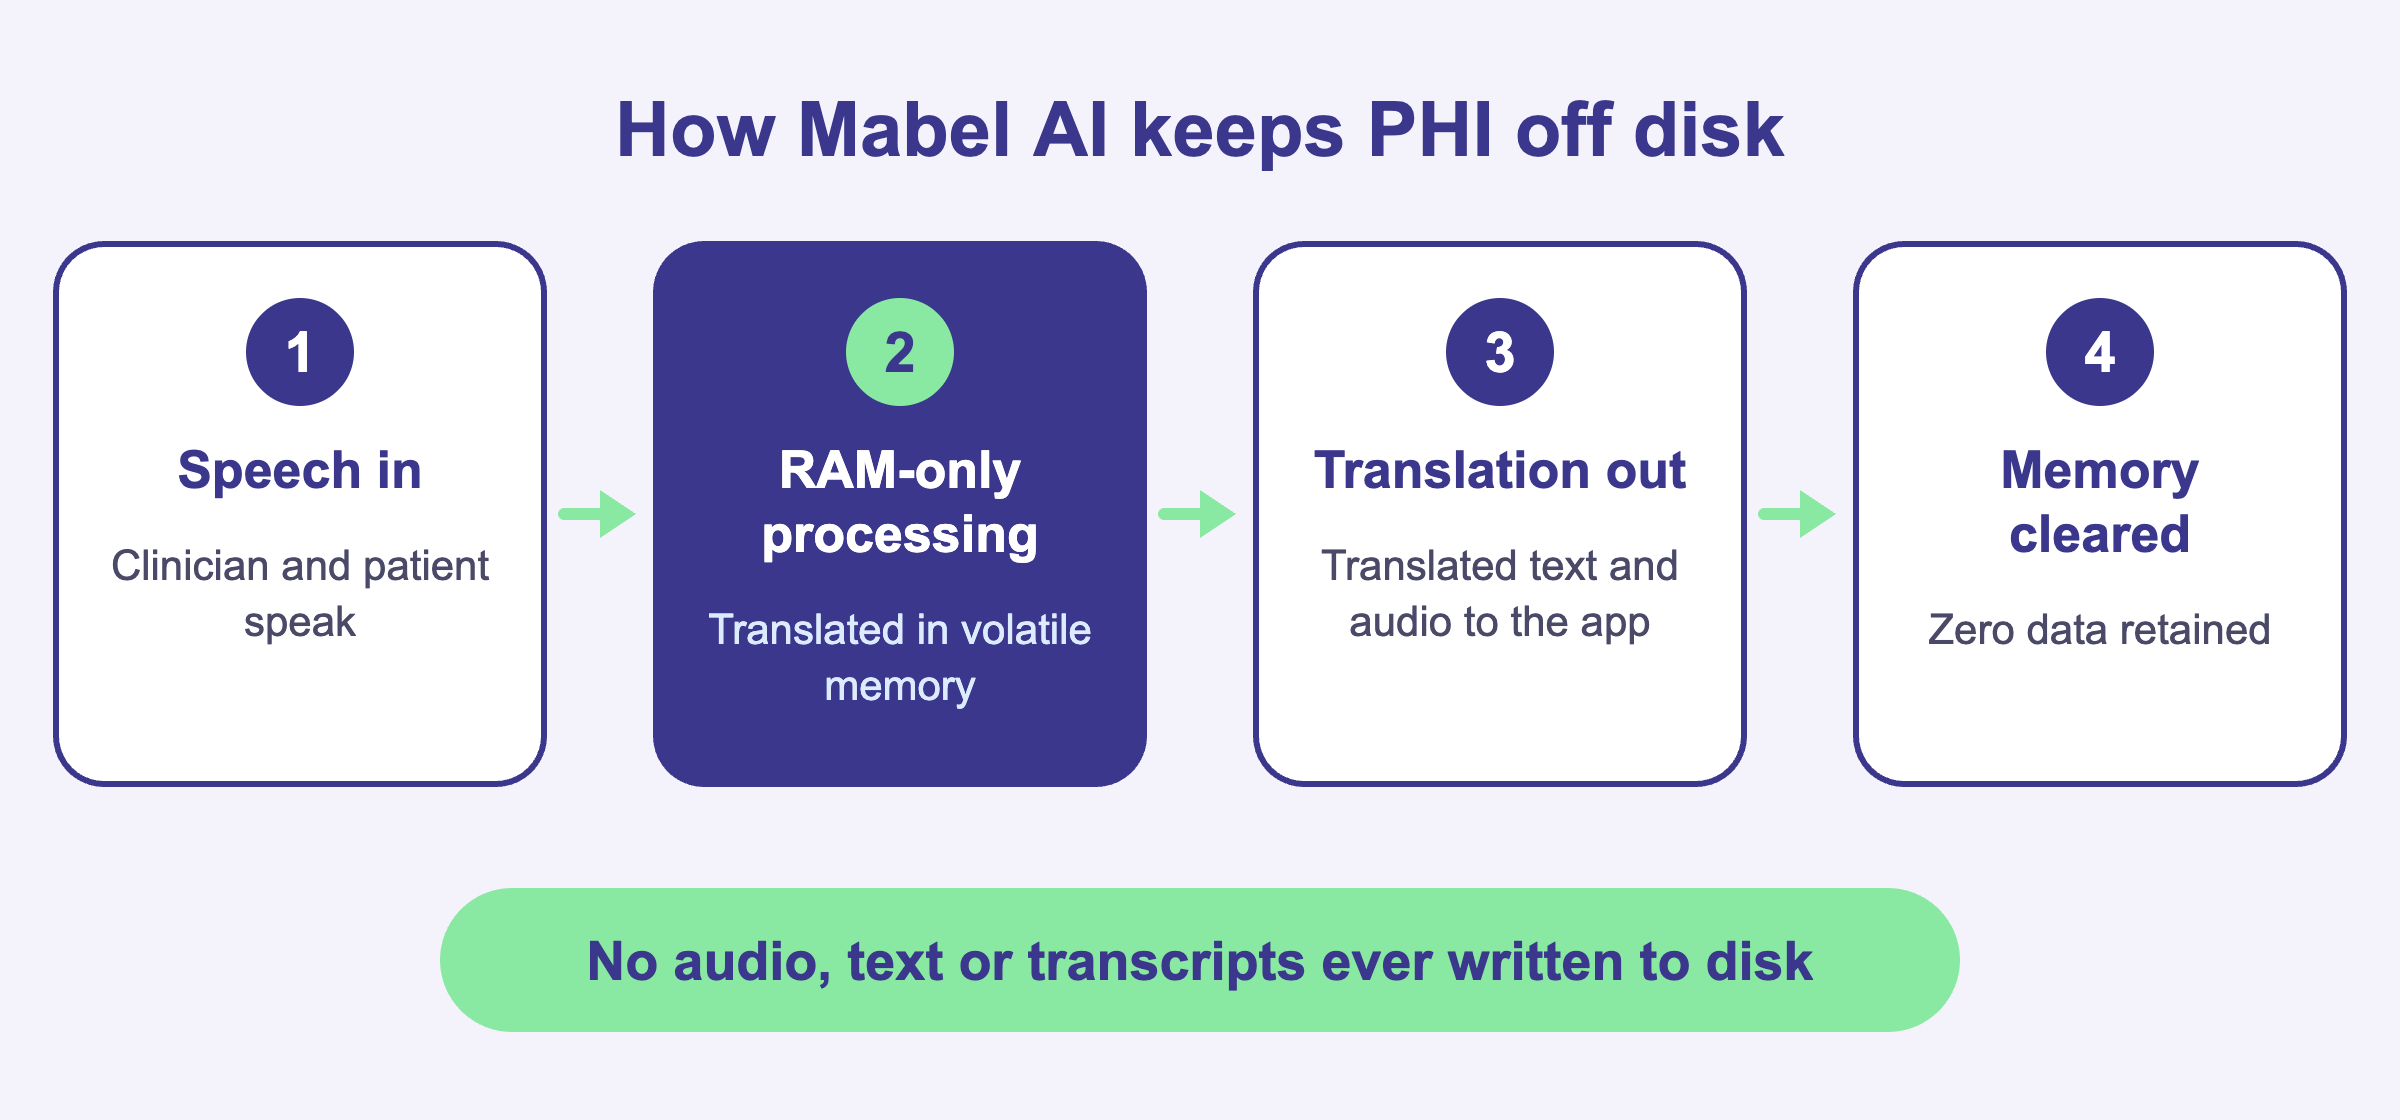
The Mabel AI Privacy Advantage: True Zero Data Retention
Unlike standard translation apps that log patient interactions or temporarily cache audio files, Mabel AI is engineered with a strict In-Memory (RAM-only) Processing Architecture. This means:
- No Disk Writes: We process all audio and text exclusively in main memory. No conversation data, audio files, or transcripts are ever written to disk, flash storage, or database logs.
- True Zero Data Retention: Once the translation session concludes or the text is pushed to your EHR, the RAM is cleared. There is absolutely no residual data left behind to be breached.
- No AI Training on PHI: Because we retain zero data, your confidential medical consultations can never be used to train AI models.
Flexible Deployment for Maximum Security
Mabel AI eliminates the severe HIPAA violation risks associated with unsecured external servers by offering flexible, highly secure deployment architectures tailored for healthcare environments:
- On-Premise Infrastructure: For organizations requiring absolute data sovereignty, Mabel AI runs locally within your hospital's secure Kubernetes infrastructure via Docker containers. Data never leaves your firewall.
- Secure SaaS (Cloud): Our cloud infrastructure is fully compliant with modern healthcare standards, utilizing dedicated, highly secure endpoints. Crucially, we do not use Microsoft Azure, OpenAI, or other third-party Big Tech APIs for our AI processing. Your data stays exclusively within Mabel's secure environment.
- On-Device Mobile App: Deployed securely to clinician devices, allowing for real-time translation at the point of care with minimized external network reliance.
How We Satisfy HIPAA Regulations
Our platform is engineered to align strictly with the US Health Insurance Portability and Accountability Act (HIPAA) requirements:
The HIPAA Privacy Rule
We ensure that all individually identifiable health information (PHI) remains strictly confidential. Whether utilizing our on-premise, secure SaaS, or on-device solutions, PHI is protected against unauthorized access and is never exposed to public AI APIs or external tech giants like Microsoft.
The HIPAA Security Rule
Mabel AI implements rigorous Technical, Physical, and Administrative safeguards:
- Technical: End-to-end encryption and in-memory-only processing guarantee that your data cannot be extracted from storage drives.
- Physical: Flexible deployment options mean you control where the data is processed, whether in your secure data center or via our independent, secure SaaS architecture—completely avoiding third-party commercial AI hubs.
- Administrative: We execute comprehensive Business Associate Agreements (BAAs) with covered entities prior to deployment.
The HIPAA Breach Notification Rule
Because Mabel AI operates on an in-memory, zero-retention policy across all deployment models, no conversation data is ever written to disk. This fundamentally eliminates the risk of centralized patient databases being breached, drastically minimizing your organization’s risk profile and liability.
Frequently Asked Questions (FAQ)
Is Mabel AI HIPAA compliant?
Yes. Mabel AI is fully HIPAA-compliant across our on-premise, secure SaaS, and on-device deployment models. Protected Health Information (PHI) is kept completely secure and encrypted.
Does Mabel AI store or record patient conversations?
No. Mabel AI operates on a strict zero-data-retention policy. All translations are processed entirely in main memory (RAM). Absolutely no conversation audio or text is written to disk. Once the session ends, the memory is cleared instantly.
Does Mabel AI send data to Microsoft, Azure, or OpenAI?
No. Unlike many AI wrappers, we do not use Microsoft Azure Cognitive Services, OpenAI, or any other Big Tech APIs for AI inference. Our models are proprietary and fully independent, ensuring that patient data never leaves your secure environment or passes through third-party commercial AI pipelines.
See HIPAA-Compliant Medical Interpretation in Action
Ready to protect patient privacy without slowing down care? Contact our team to book a demo, compare plans on our pricing page, or learn more about Mabel AI.